My name is Septio Noerdiansyah, known online as RyuuKhagetsu — a passionate cybersecurity professional with over 5 years of experience in penetration
testing, vulnerability assessment, and red teaming. My journey began as a CTF enthusiast
while studying Computer Science, and quickly evolved into a professional career in security.
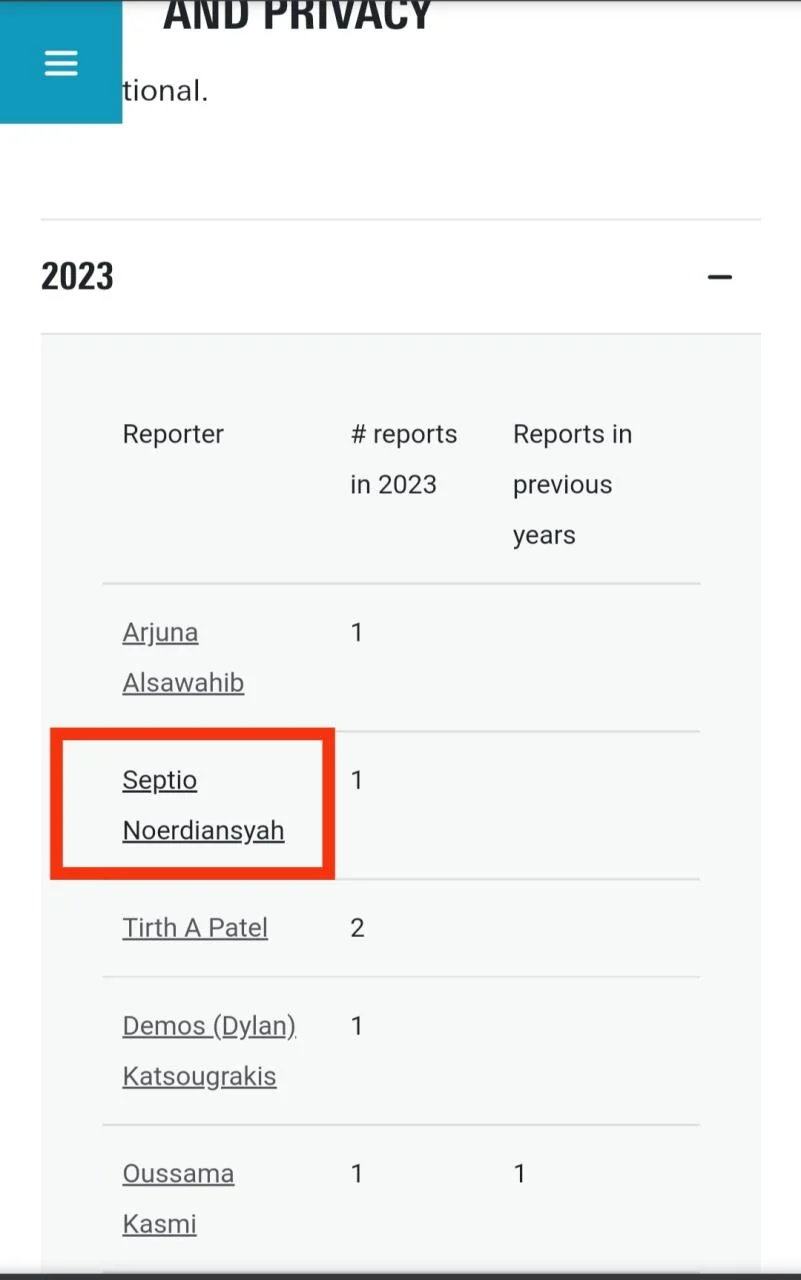
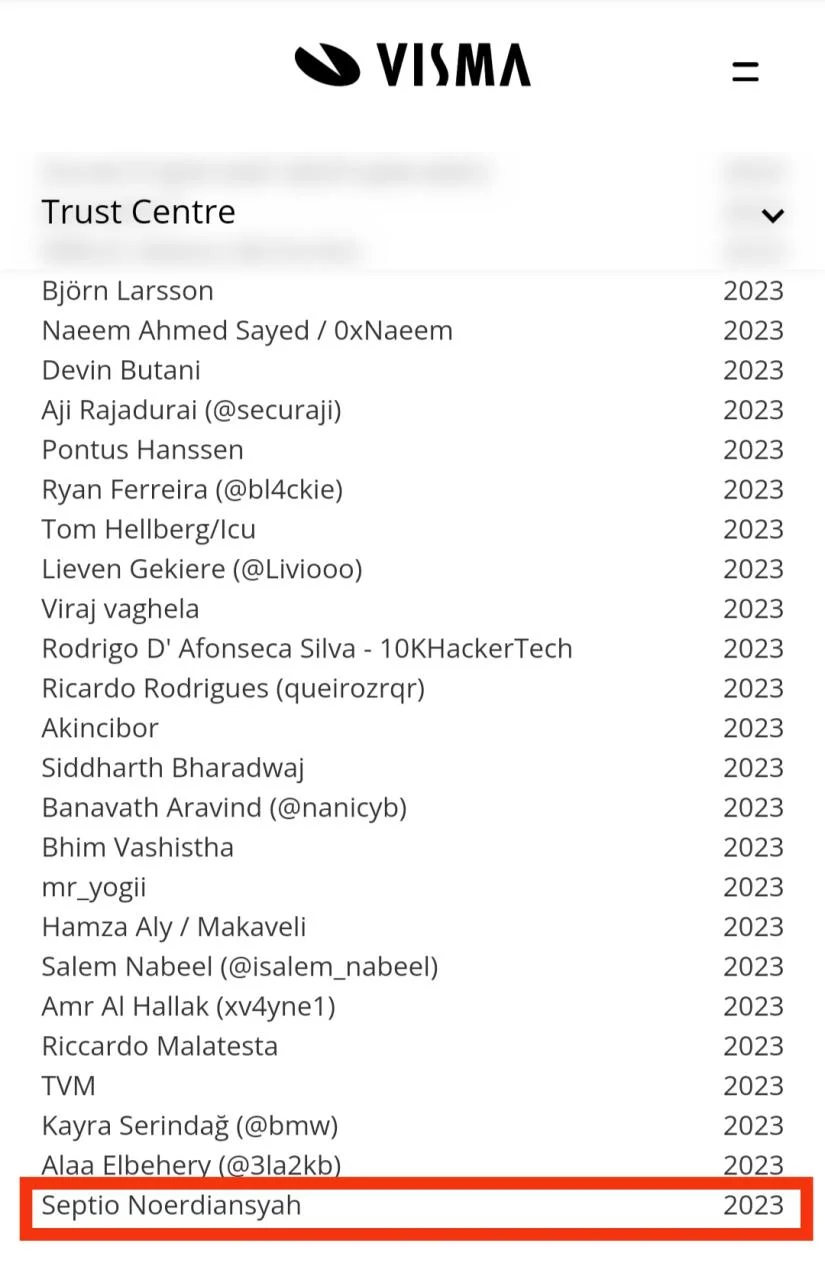
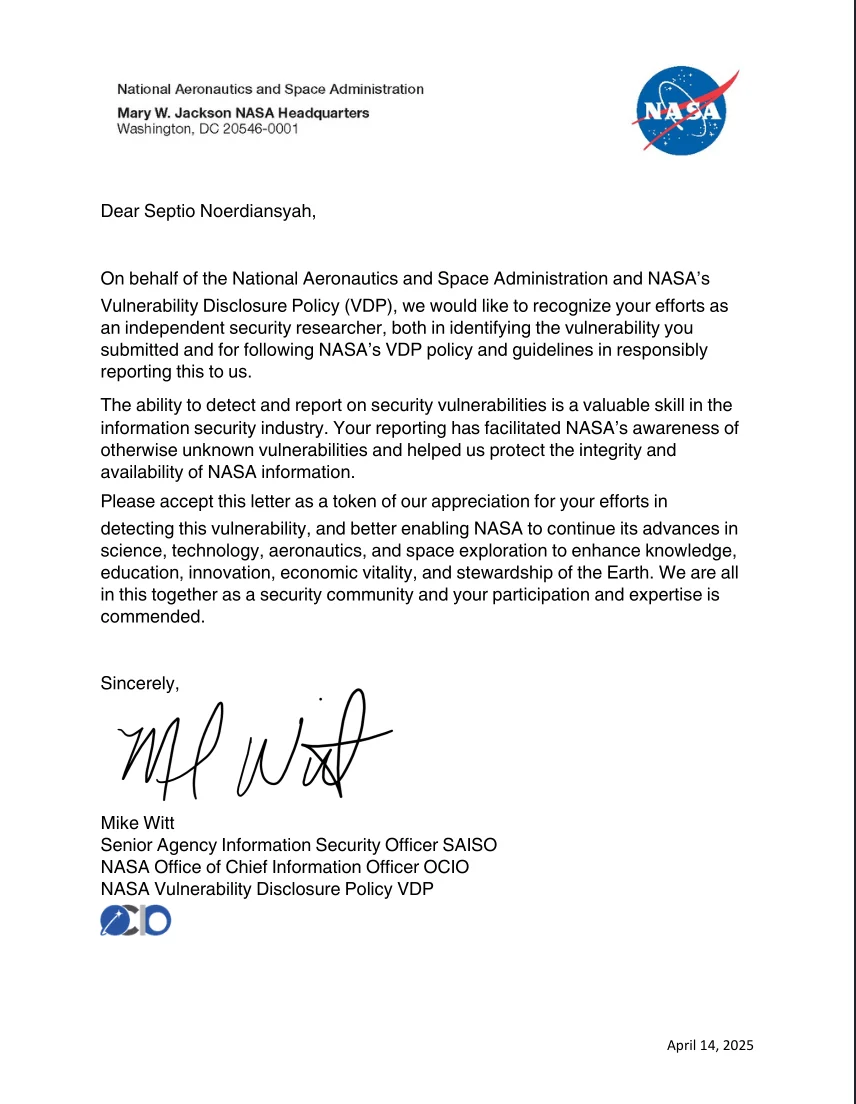
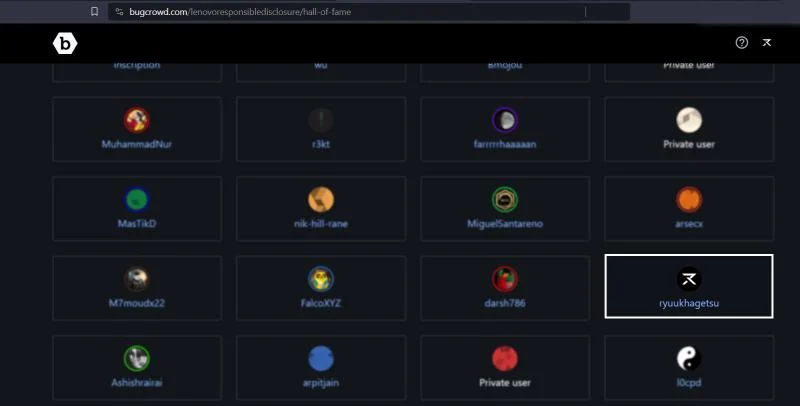
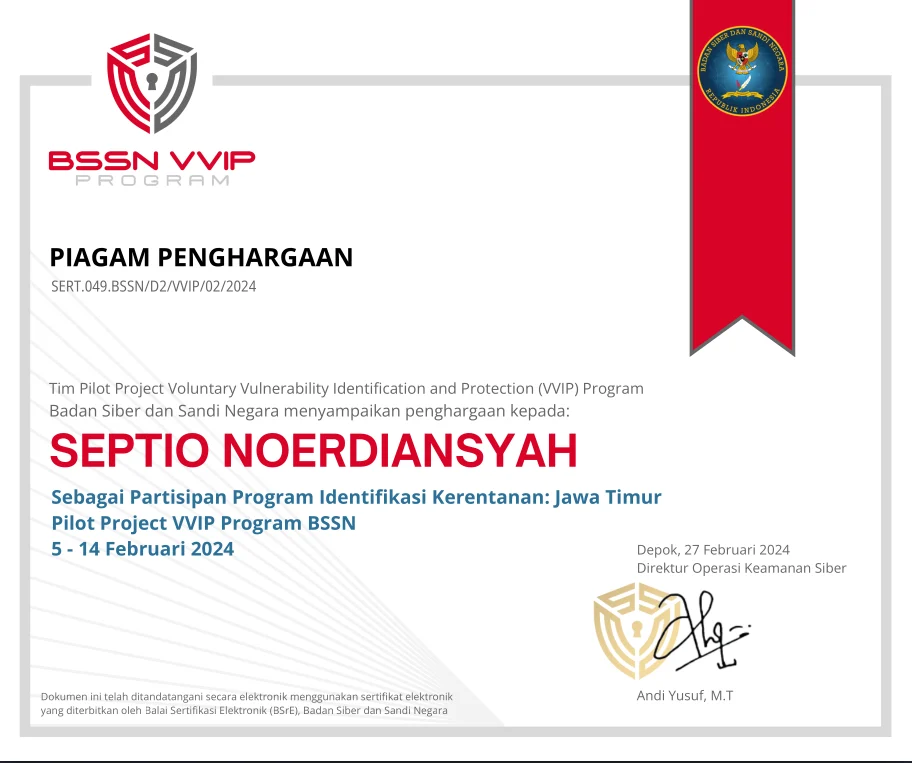
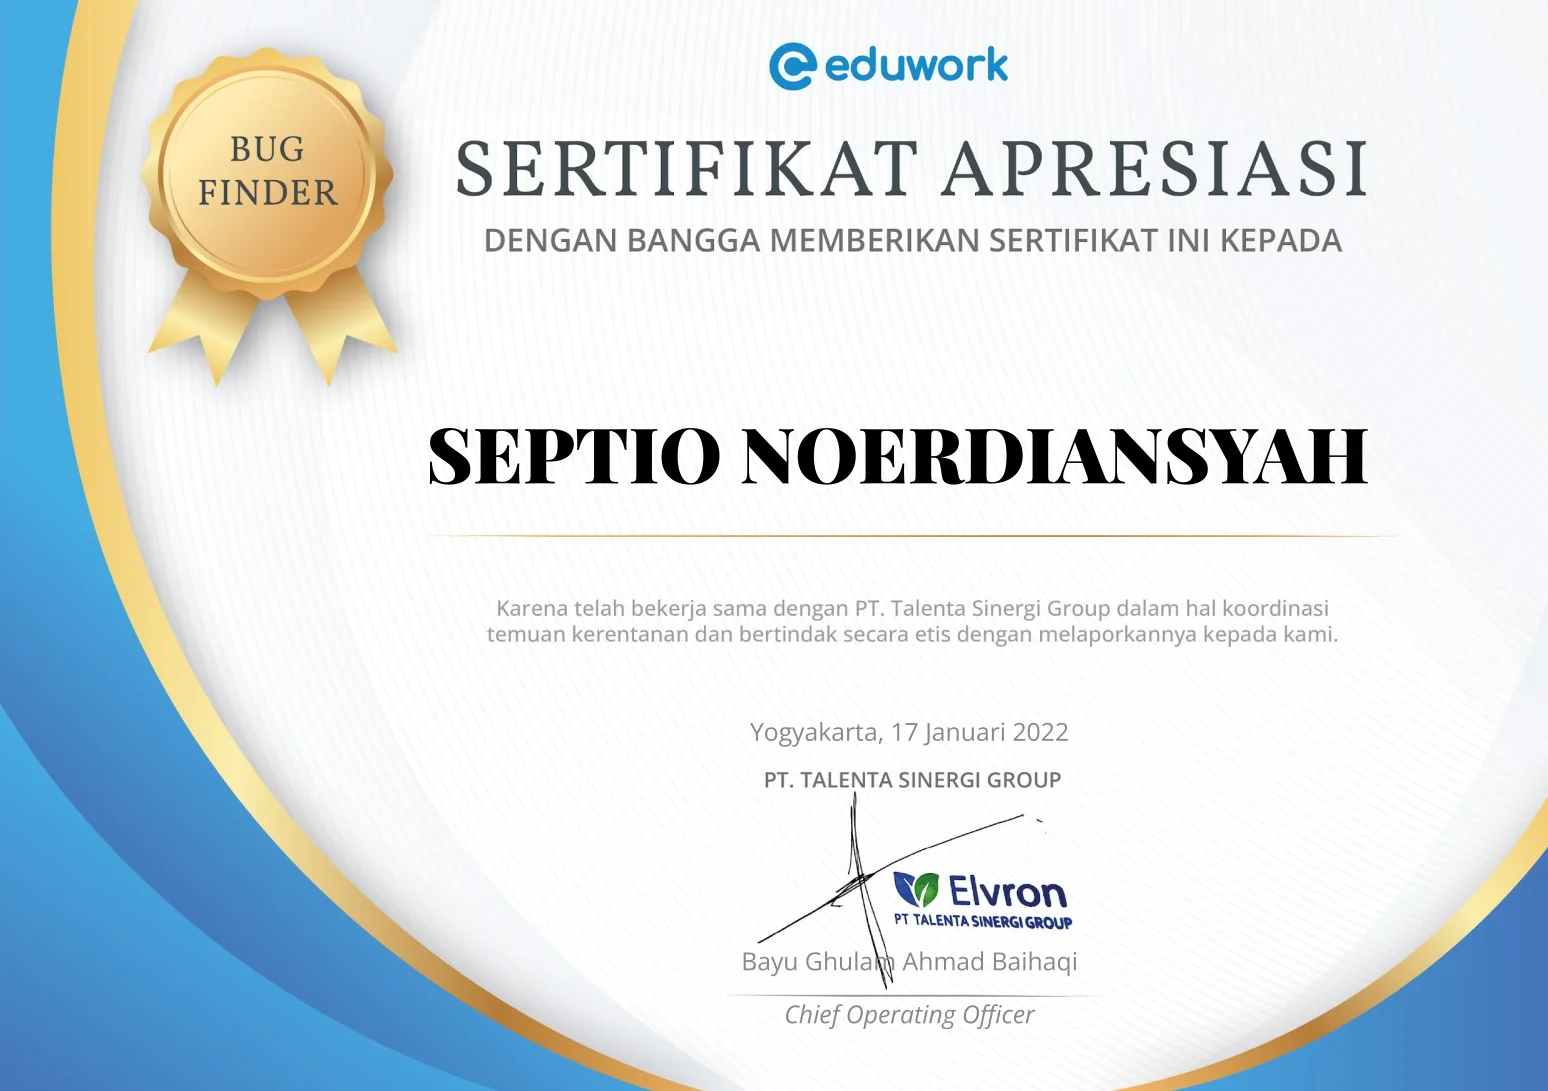
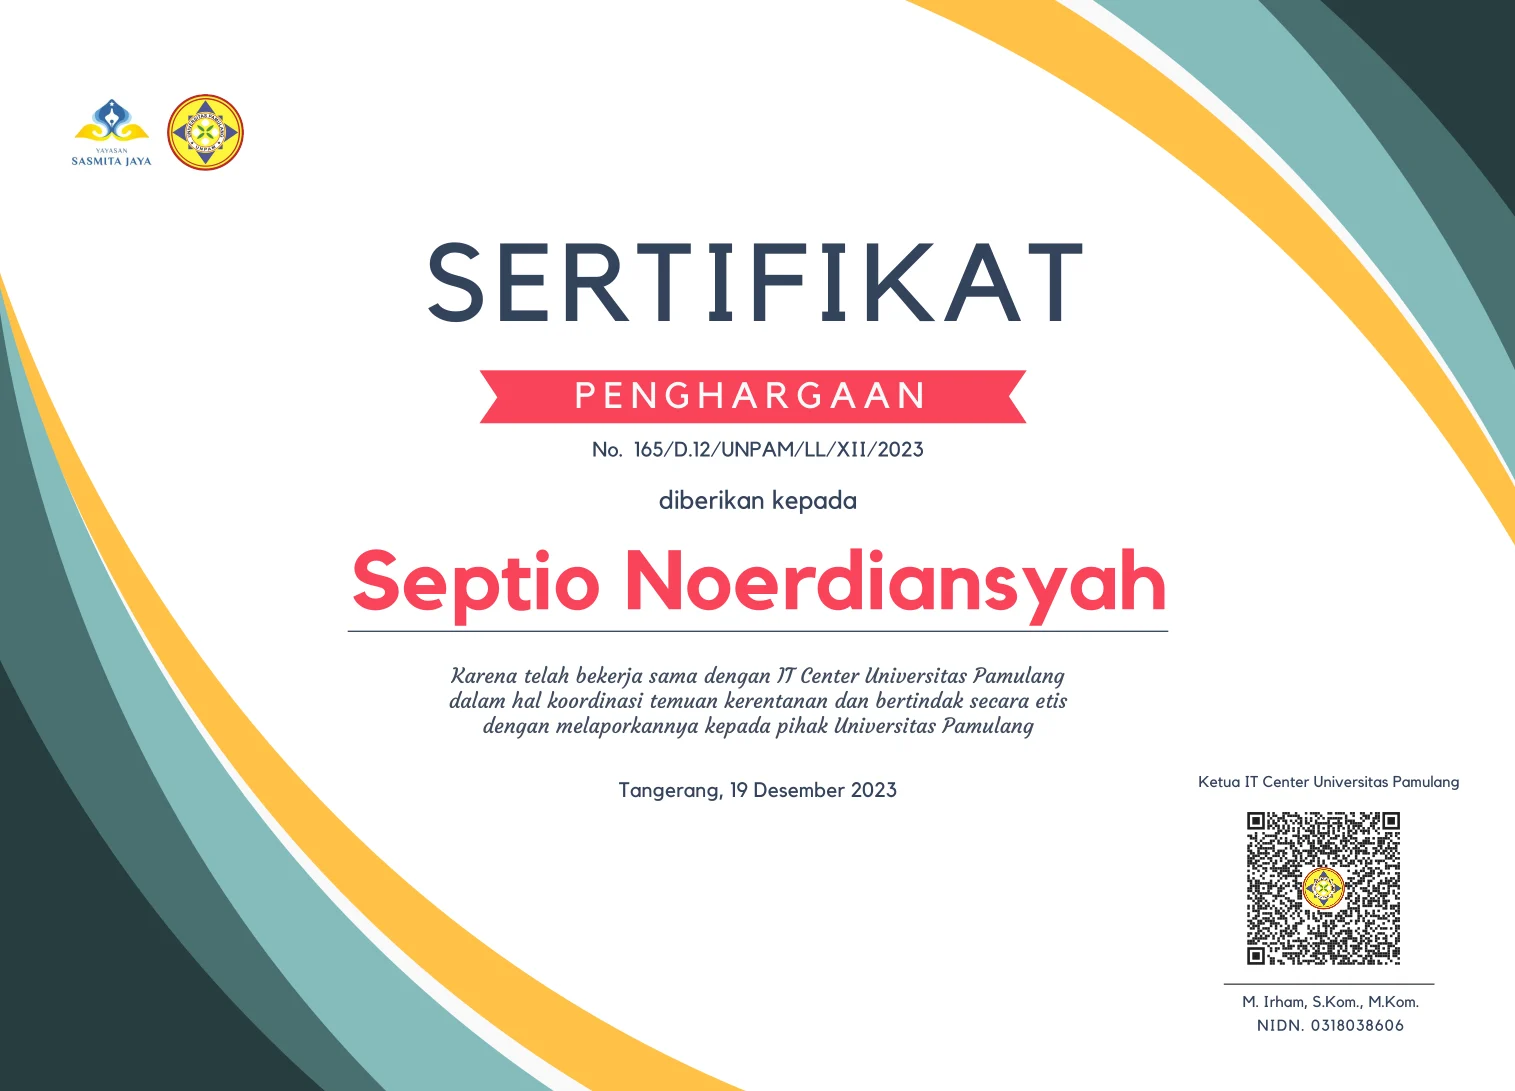
Alongside client engagements I work as an independent security researcher,
reporting vulnerabilities in widely deployed open-source software through the Patchstack
program. That research has so far resulted in 4 published CVEs across the
WordPress plugin ecosystem — each coordinated with the vendor and disclosed only after a
patch was released.
My mission is to help organizations strengthen their security posture by identifying and
mitigating vulnerabilities before they can be exploited by malicious actors. I believe in
responsible disclosure and ethical hacking principles.
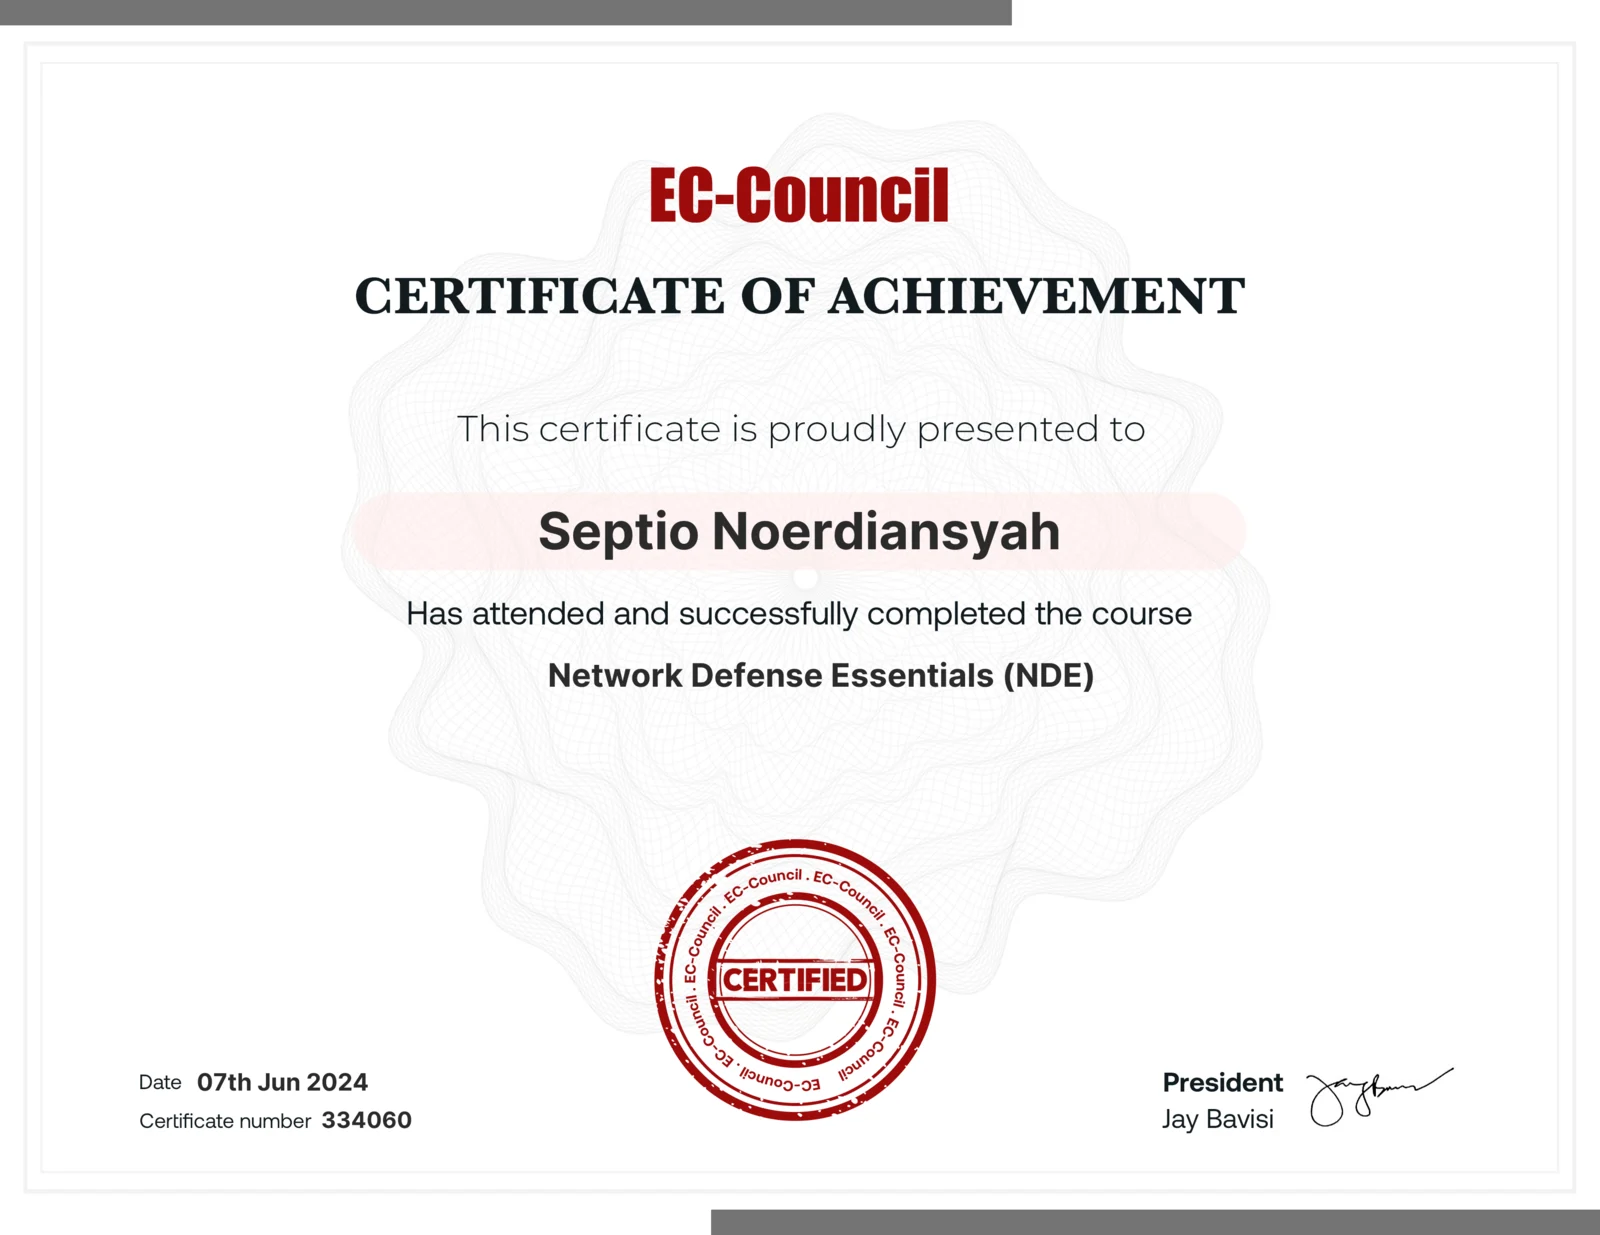
Certifications
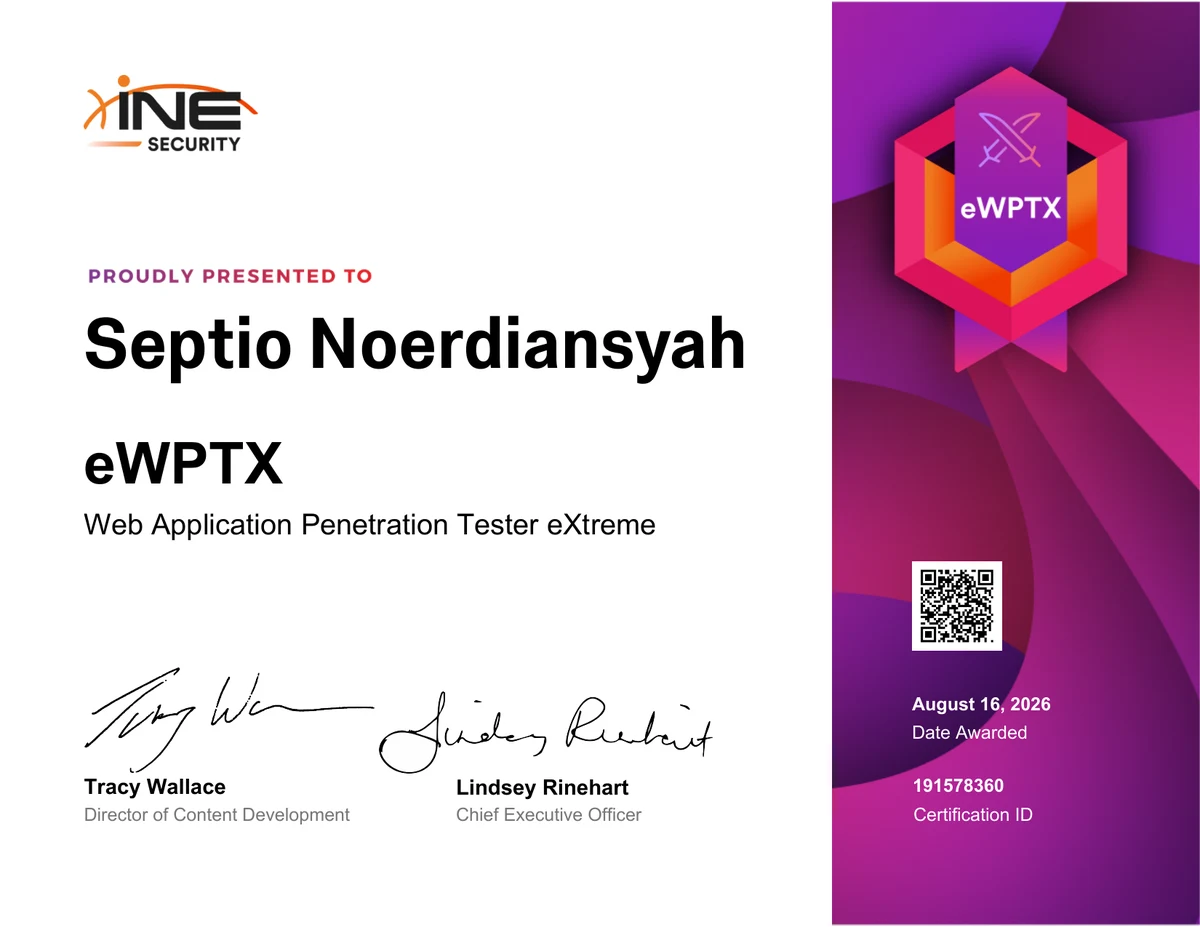
- INE Web Application Penetration Tester
eXtreme (eWPTX)
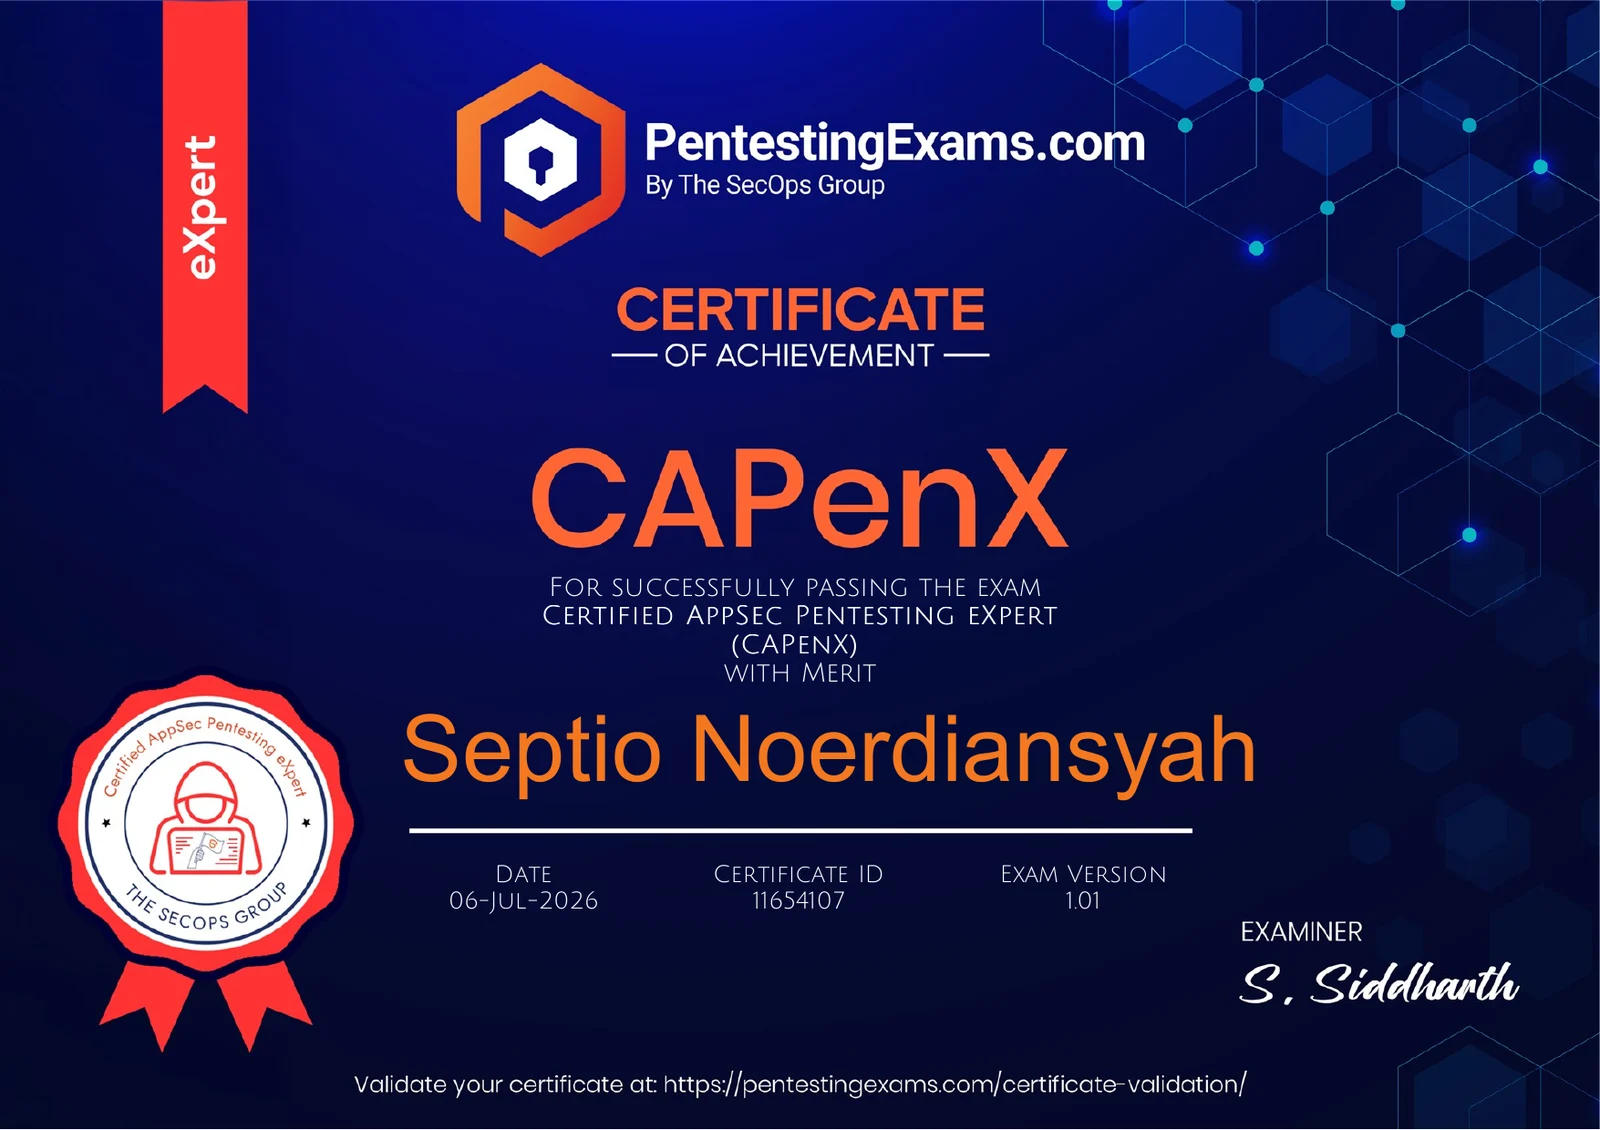
- SecOps Group Certified AppSec Pentesting
eXpert (CAPenX)
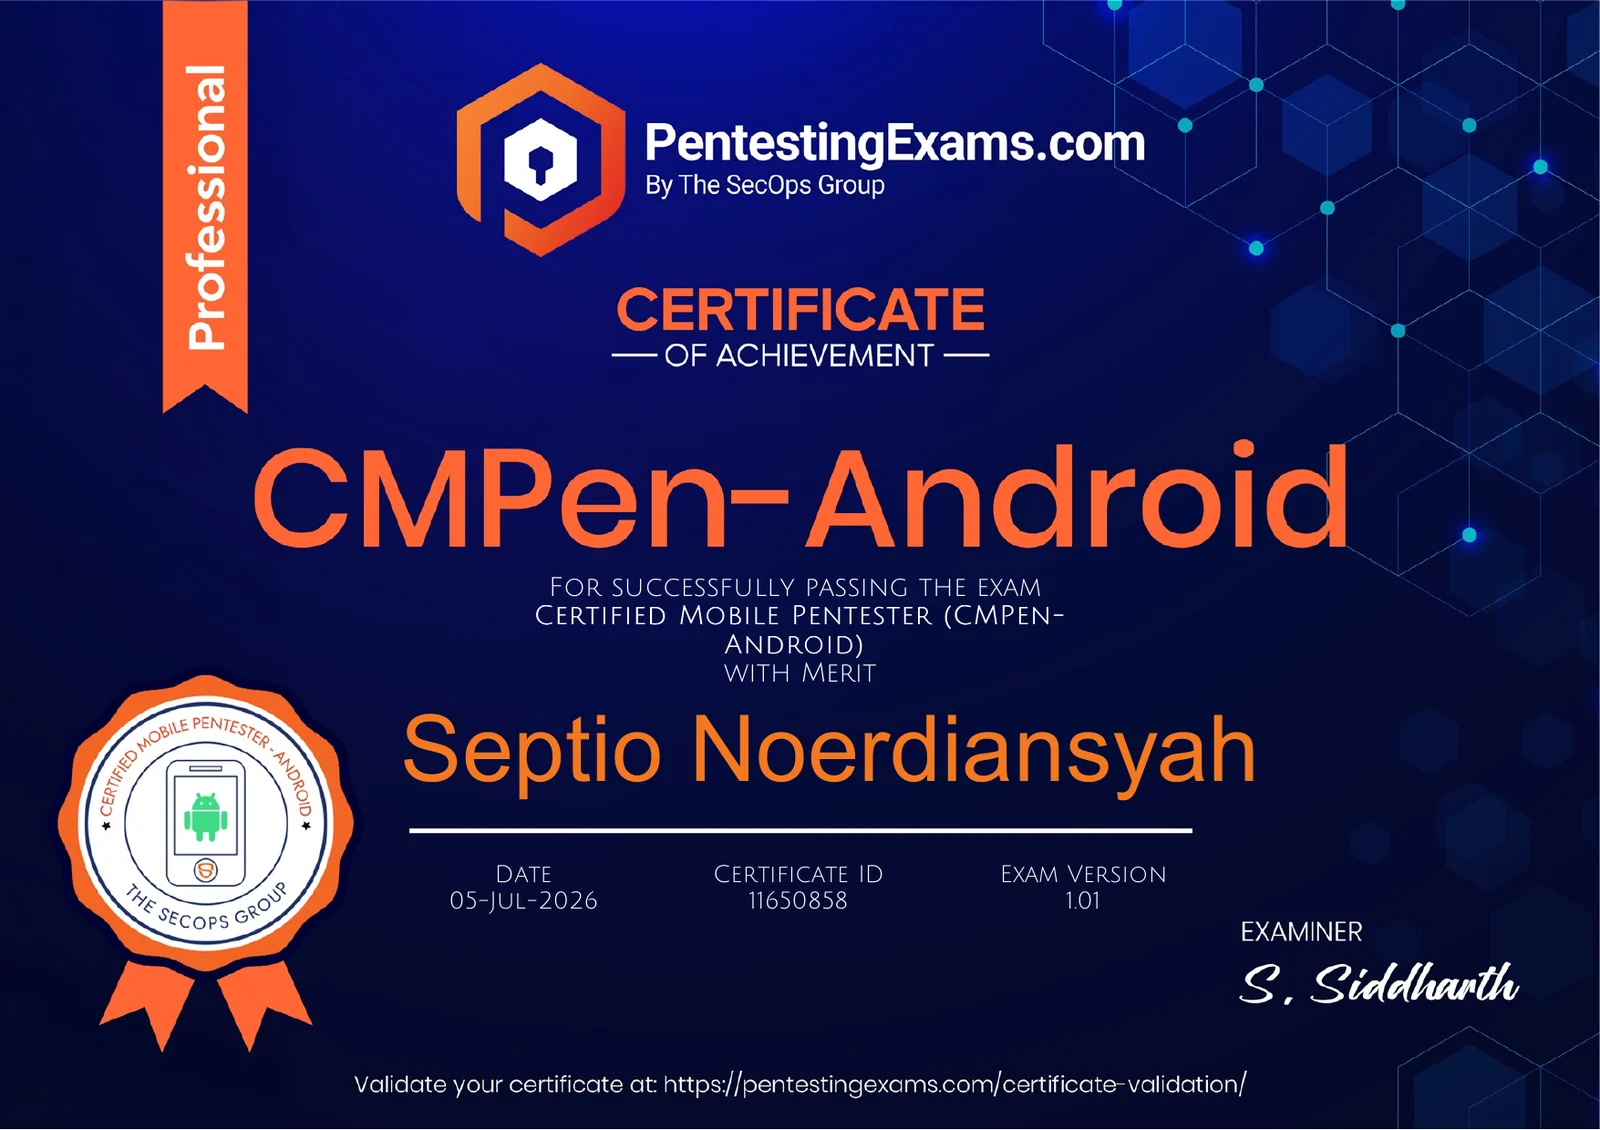
- SecOps Group Certified Mobile Pentester
(CMPen-Android)
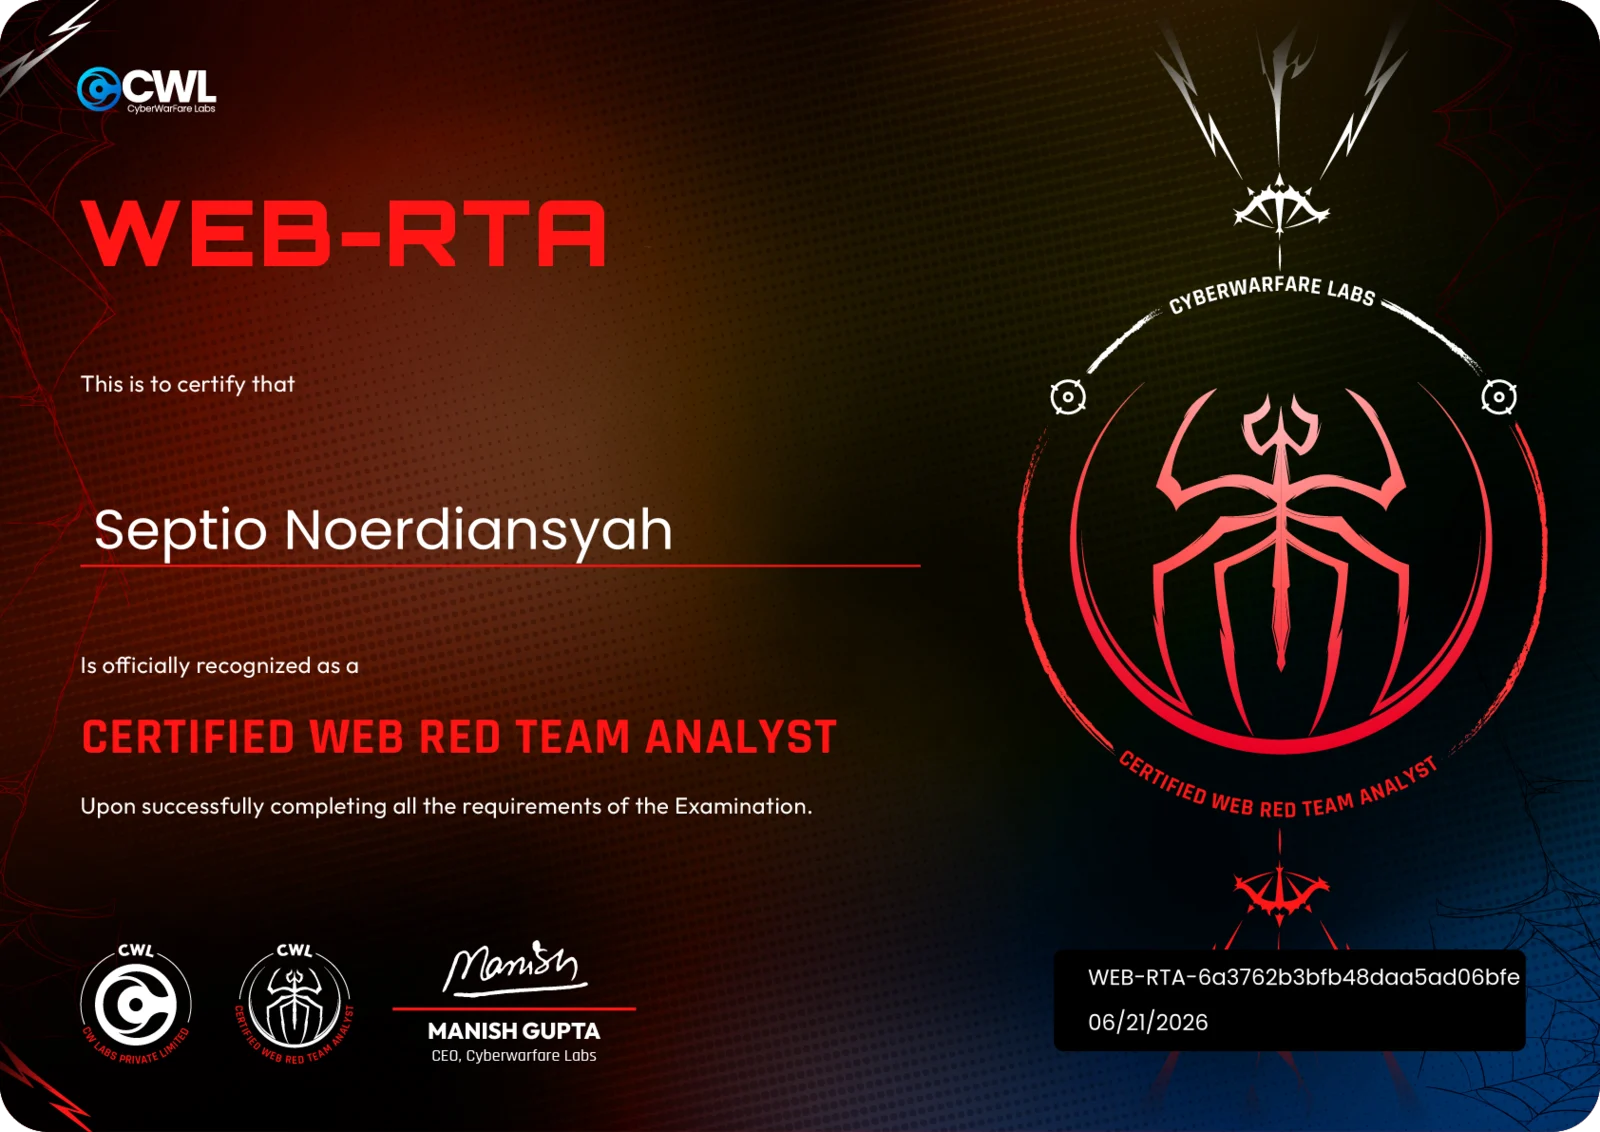
- Cyberwarfare Labs Certified Web Red Team
Analyst (WEB-RTA)
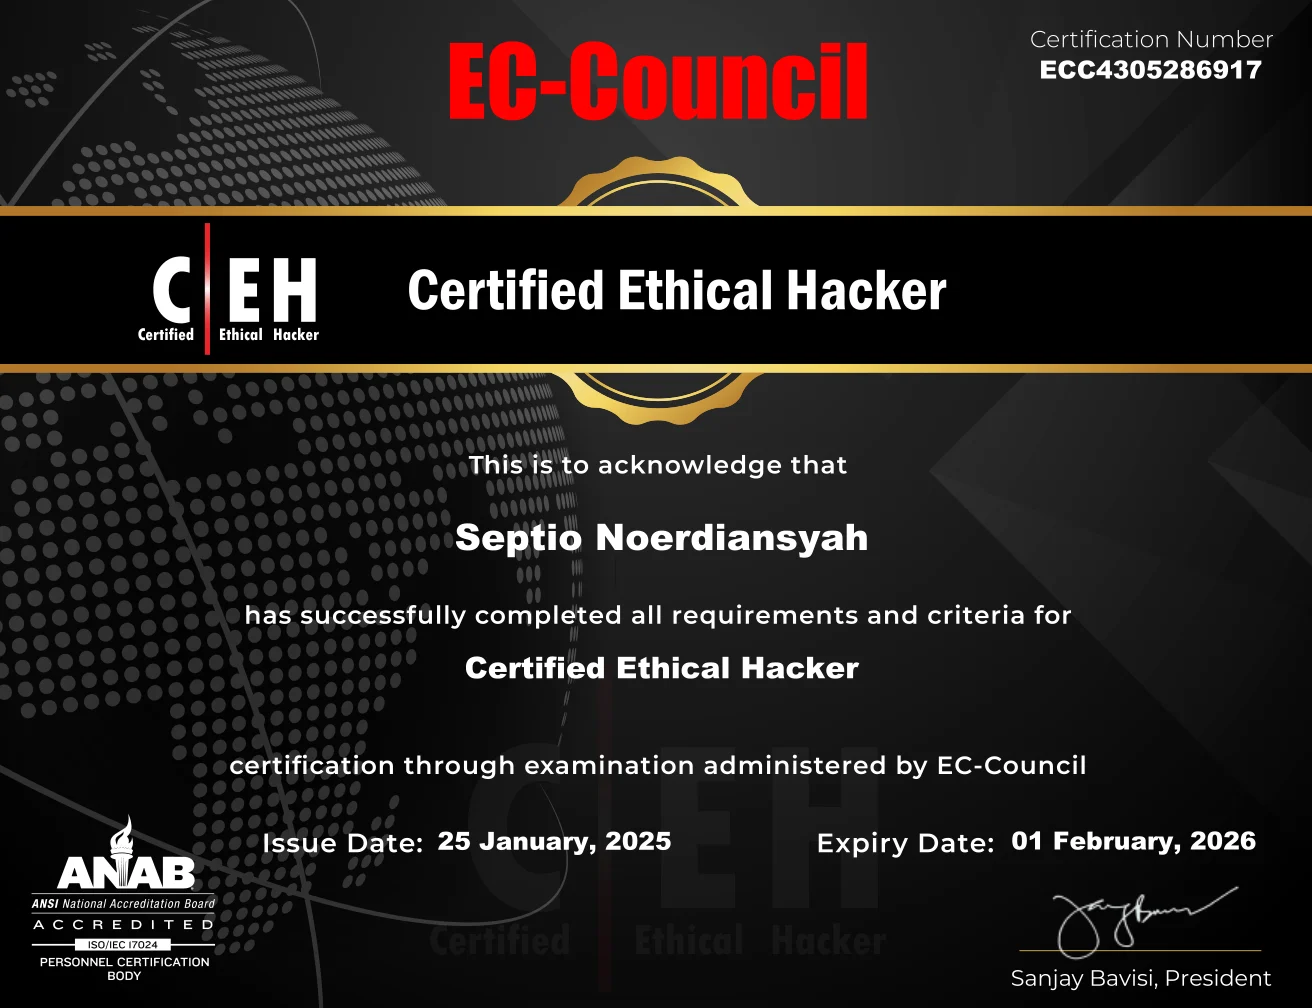
- Certified Ethical Hacker (CEH) v13
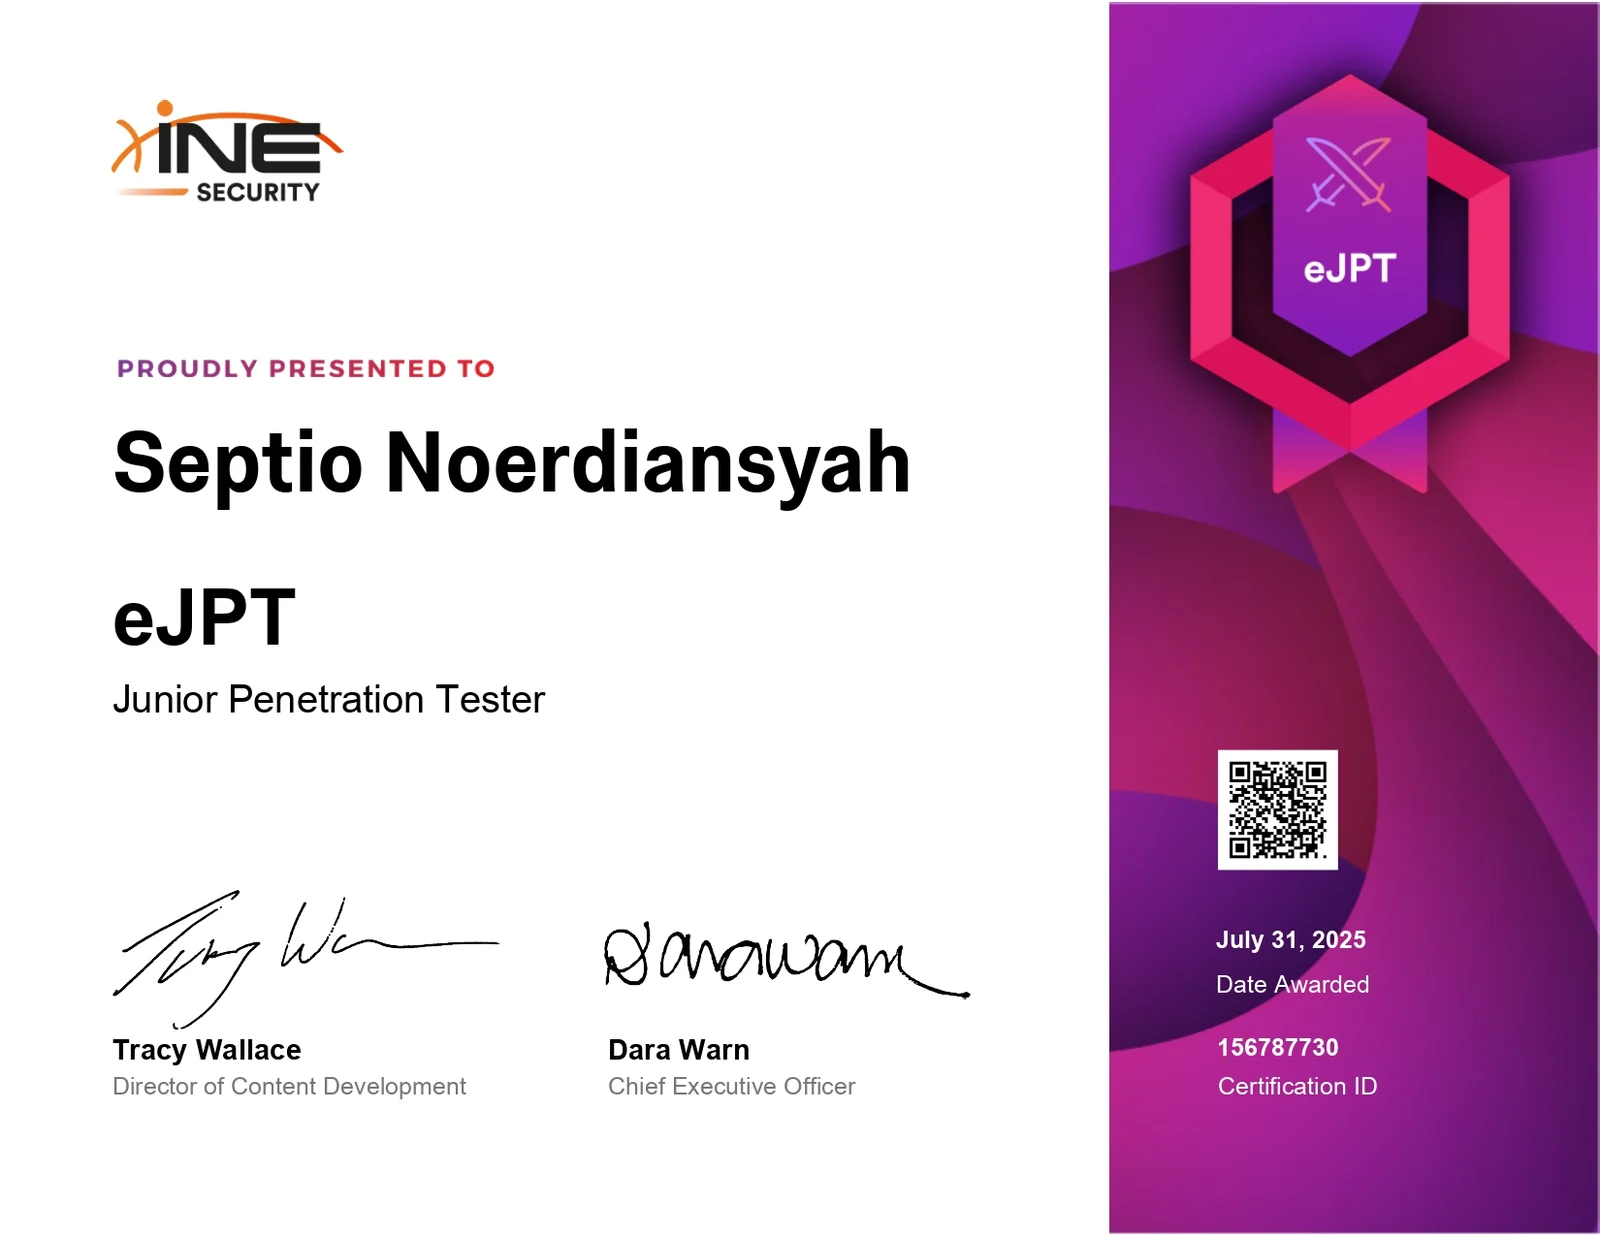
- INE eLearnSecurity Junior Penetration Tester (eJPT)
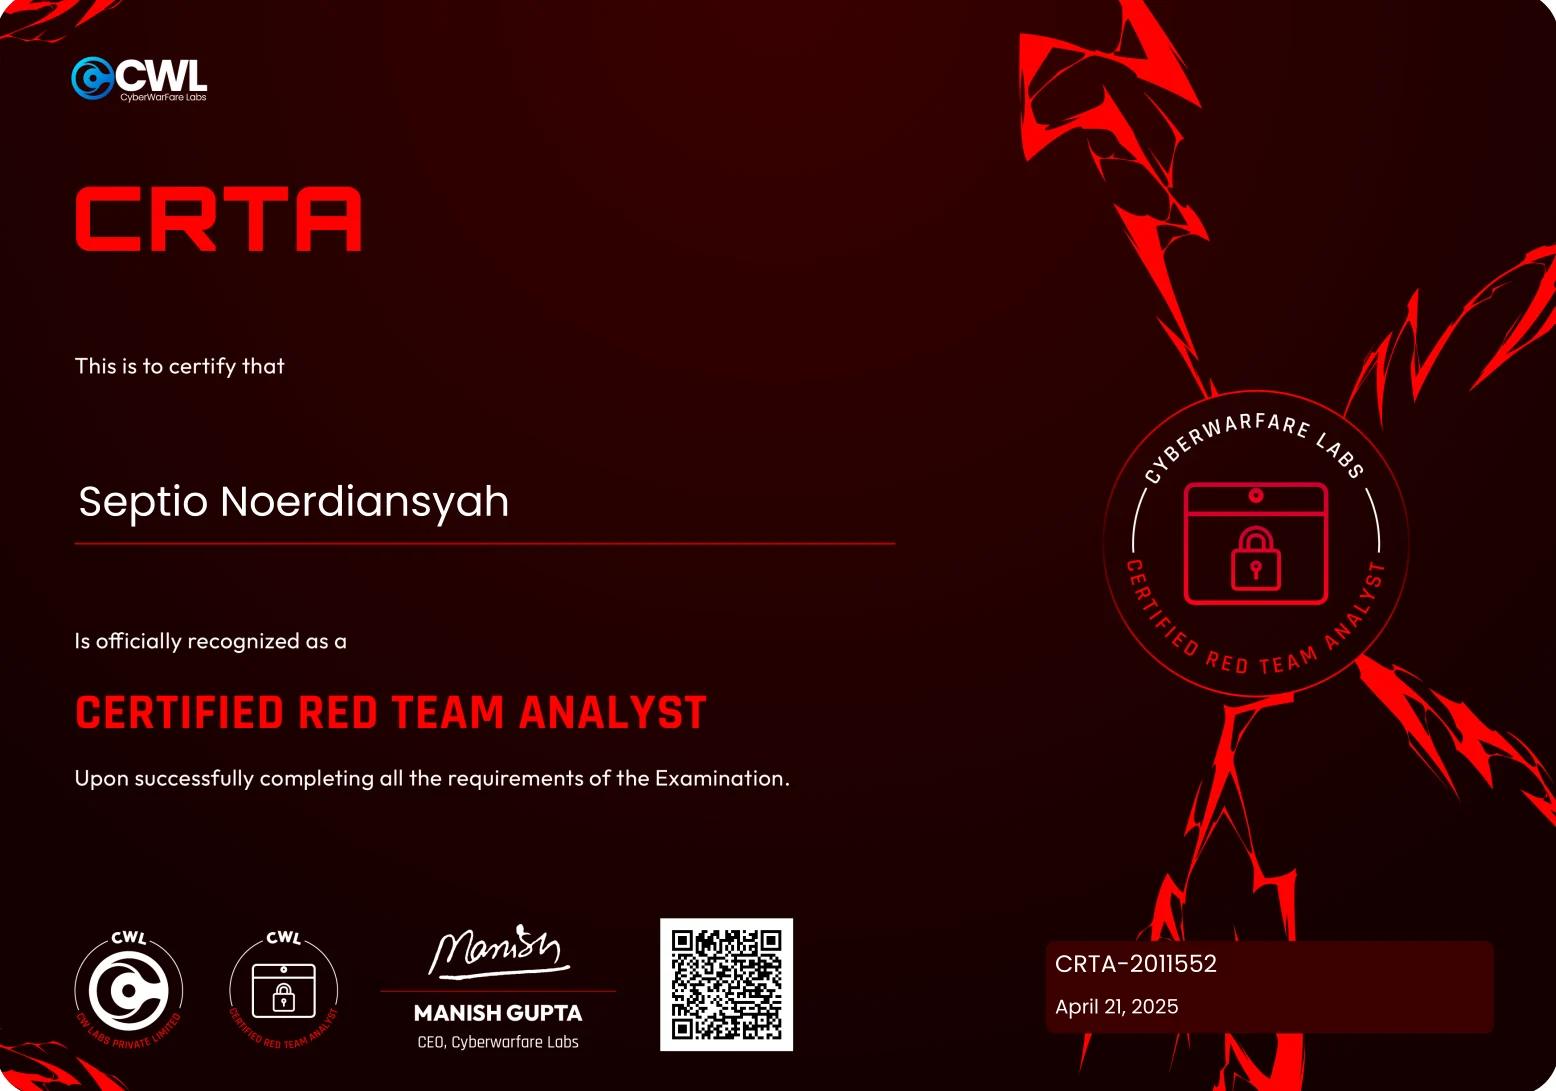
- Cyberwarfare Labs Certified Red Team
Analyst (CRTA)
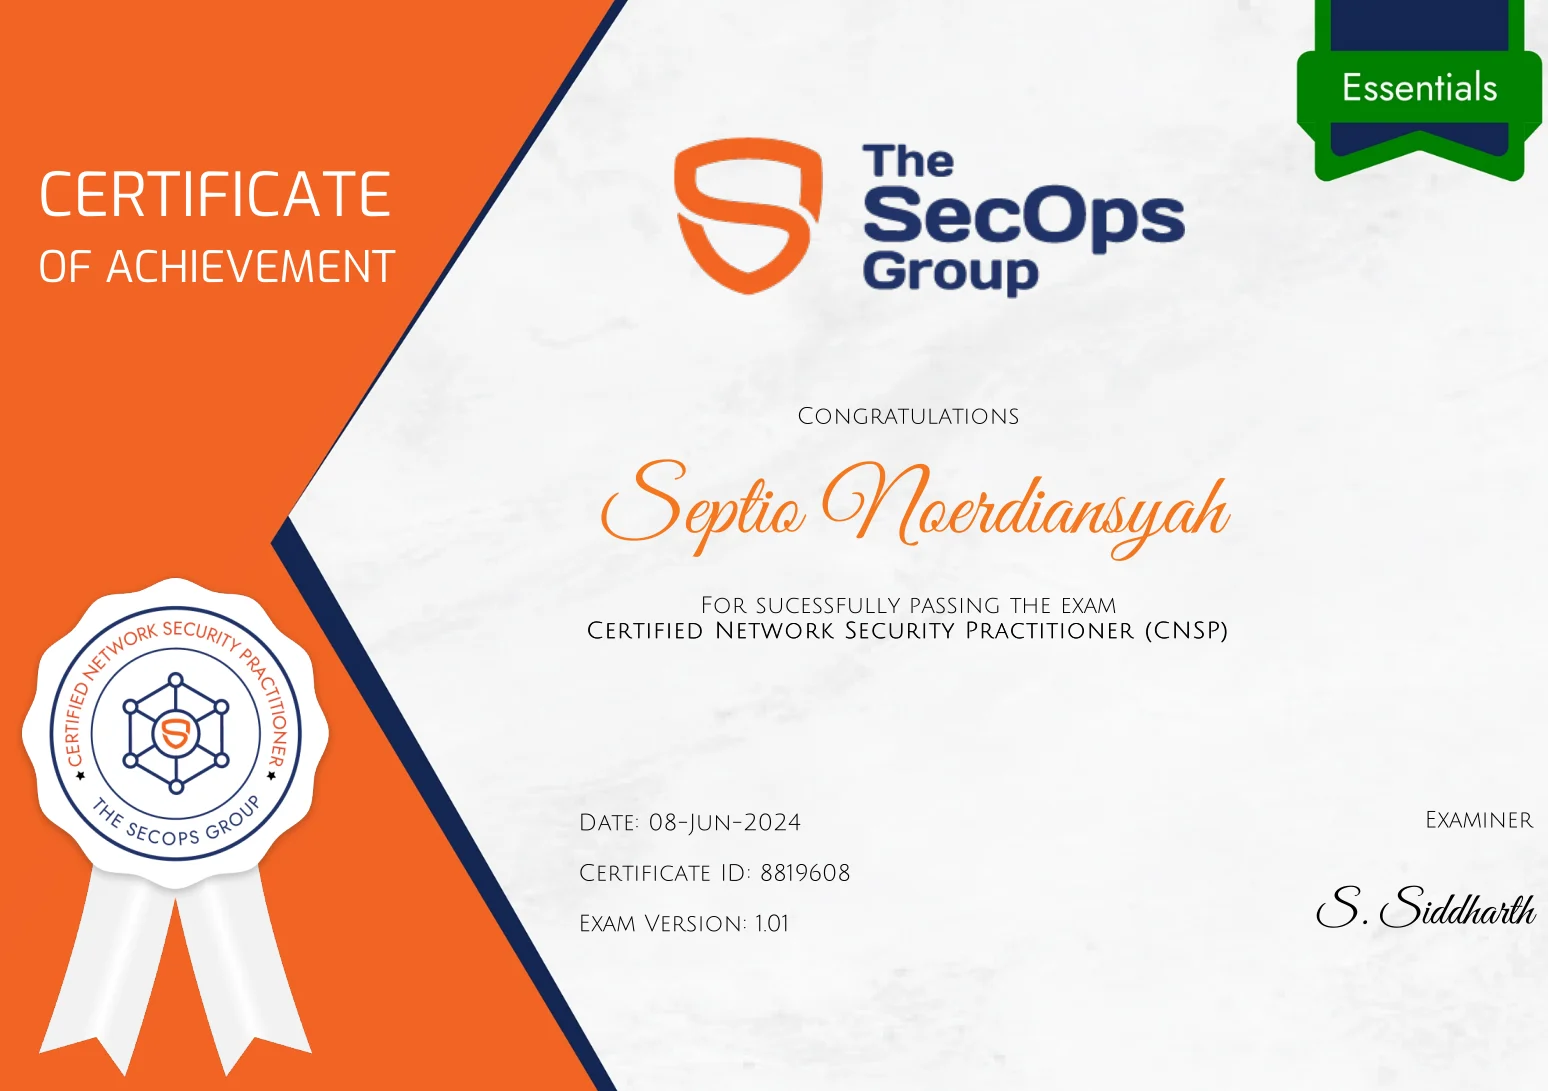
- SecOps Group Certified Network Security
Practitioner (CNSP)
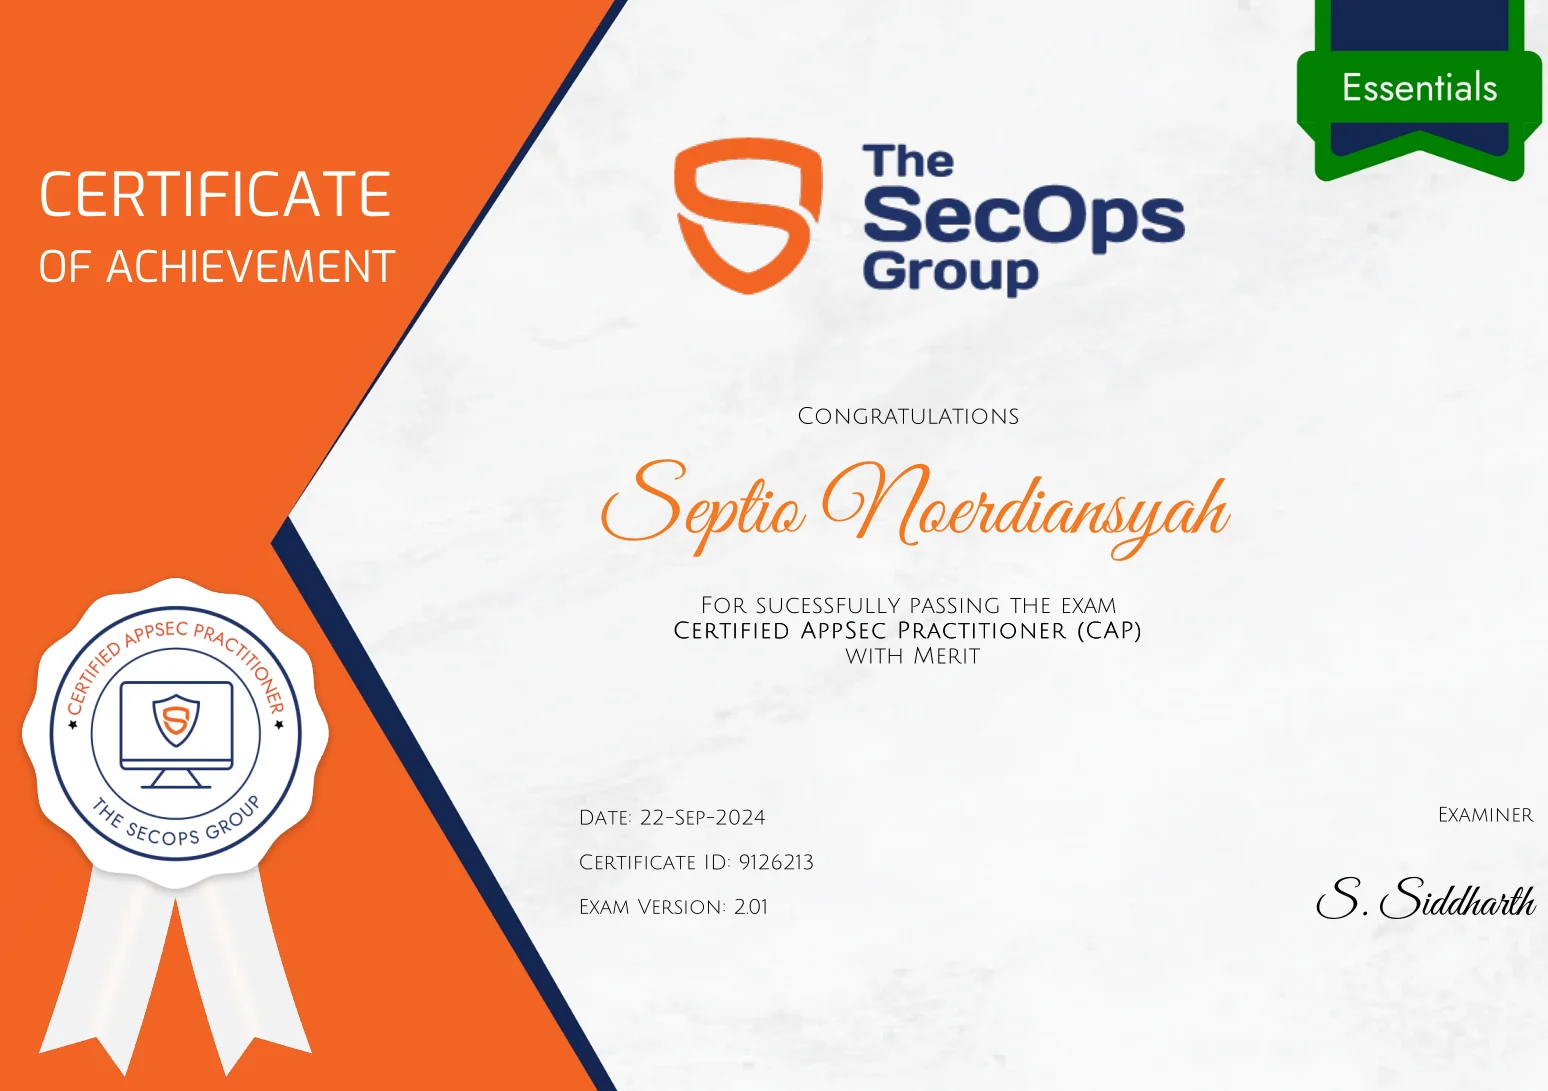
- Secops Group Certified AppSec Practitioner
(CAP)
- Cyberwarfare Labs Certified Process
Injection Analyst (CPIA)
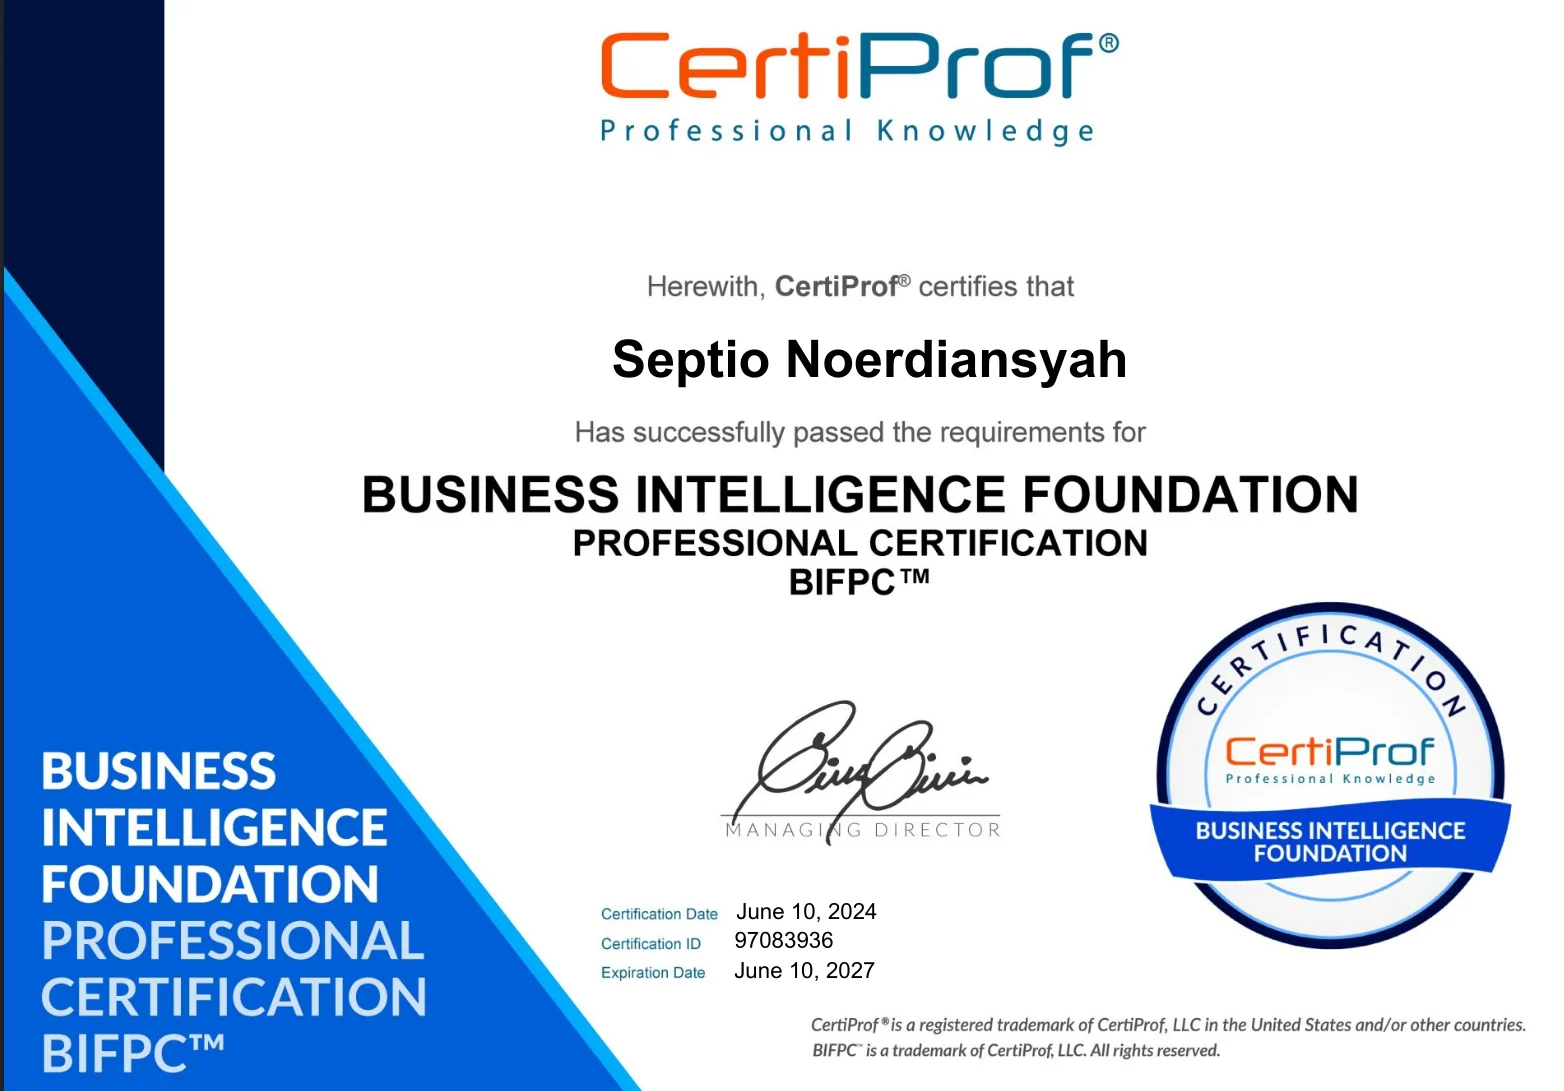
- Cybersecurity Awareness Professional
Certification (CAPC)
- OSCP (In Progress)
Favorite Tools
- Burp Suite Pro
- Metasploit Framework
- Frida & Ghidra
- Wireshark & Nmap
- Cobalt Strike & Covenant